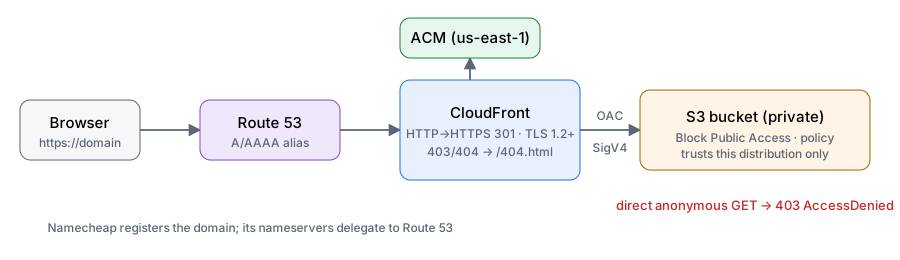
Cloud architecture
Visitors reach the site through CloudFront only. The S3 bucket stays private; CloudFront signs origin requests with Origin Access Control.
Follow a request
Step through what happens when someone opens the site.
- DNS. Route 53 answers the apex query with an alias to the CloudFront distribution.
- TLS. CloudFront presents the ACM certificate (issued in us-east-1) via SNI; TLS 1.2+ only.
- Redirect. Plain HTTP requests receive a 301 to the HTTPS URL.
- Cache. An edge location serves cached objects or forwards a miss to the origin.
- Origin. CloudFront signs the S3 request (SigV4, OAC); the bucket policy only trusts this distribution.
- Errors. A missing key returns 403 from S3, which CloudFront maps to the custom 404 page.
Why each service
- S3 stores files durably with no server to run.
- CloudFront provides HTTPS, caching, and the only public entry point.
- ACM issues and renews the TLS certificate.
- Route 53 hosts DNS and the alias to CloudFront.
Security controls
- Block Public Access on all four settings.
- Bucket policy scoped to one distribution ARN.
- Non-TLS requests to S3 denied.
- HSTS via a managed response headers policy.